Why Rule-Based Alerting Collapses Under Insider Threat's Core Problem and Behavioral Context Does Not
Behavioral analysis catches insider threats that rule-based systems miss entirely.
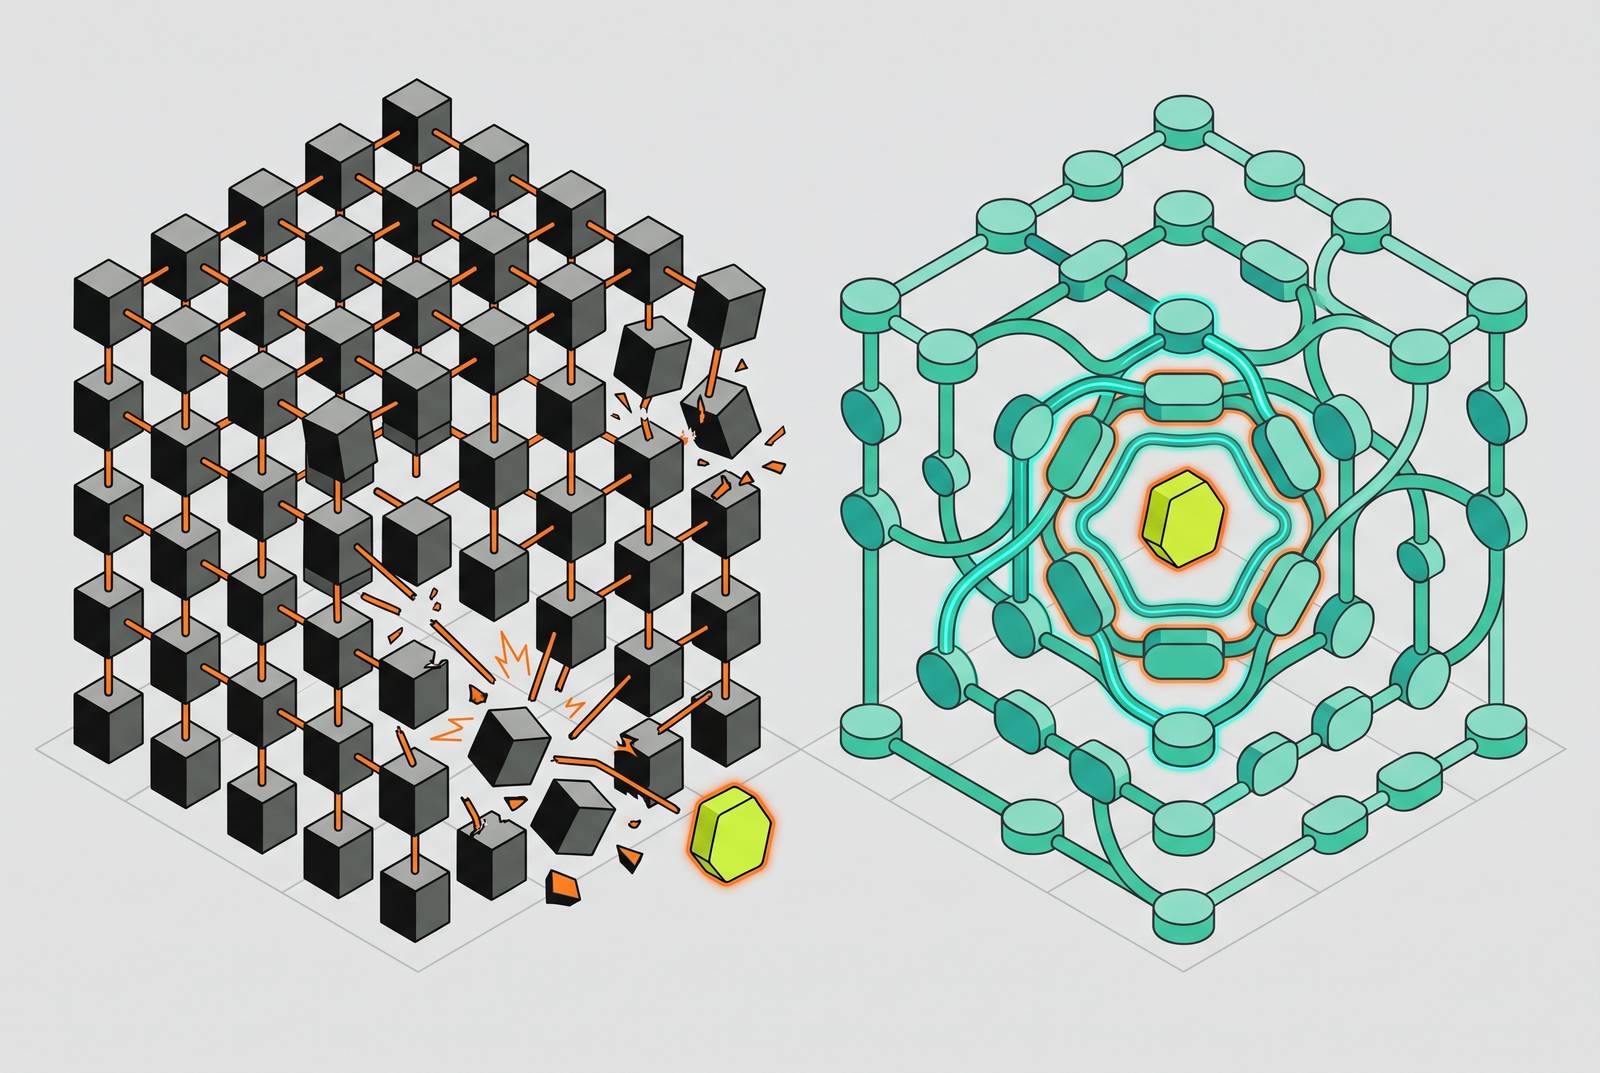
Modern insider threat platforms differ from traditional rule-based alerting by assessing whether a person’s activity is normal for their role, the data involved, and the surrounding context, rather than whether an event matches a predefined condition. This is why behavioral context addresses the structural gap that rules leave open. But behavior alone is insufficient. Effective detection must also understand the data and assemble evidence that analysts can investigate.
Why insider threats break the assumption that security tools are built on
The perimeter assumption gives security controls a clear design premise. Harmful activity comes from outside, so the first task is to distinguish authenticated access from unauthenticated access. That distinction is useful for controlling entry. It becomes insufficient when the person creating risk already has valid credentials, legitimate access, and a normal reason to use the system.
Insider threats operate inside that trust boundary. A malicious employee does not need to defeat authentication to misuse information that the job allows them to reach. A negligent employee can expose the same information without intending harm, while a compromised user’s account can give an attacker authorized access. The resulting gap is a category error when a system treats permission to access data as evidence that its use is appropriate.
That problem extends beyond permanent employees to contractors, temporary insiders whose access outlasts their engagement, and AI agents. These identities share access rights but not the same work habits, histories, or risk profiles. Insider risk is therefore a governance problem as much as a detection problem. The relevant distinction is not simply who has access, but which identity patterns and lifecycle events make that access a source of exposure.
How rule-based alerting actually works — and what it cannot see
Rule-based alerting is fast and reliable for known scenarios that can be expressed as predefined conditions. A rule can flag a copy to USB above a volume threshold, a confidential file sent to an external address, or a login outside working hours. These controls test whether a specific policy has been broken. Their limitation is that the test remains fixed unless its definition changes.
A static rule evaluates whether an event matches that definition. It does not, by itself, establish whether the action is normal for this person, with this data, at this time. A finance employee accessing engineering source code in small batches may remain below a volume threshold despite departing sharply from the role’s normal activity. Lowering the threshold changes the amount that triggers an alert.
Data movement through Slack, Salesforce, and Google Drive can form an exfiltration pattern over four months even when each action on its own is authorized. A rule watching one channel cannot reconstruct that pattern on its own. Equally, a sales director preparing for a client meeting and a disgruntled employee taking a customer list can produce identical volume signals. The missing element is context.
What rule-based failure costs security teams in practice
This mechanism creates two operational failures at once. Normal work that matches a rule creates false positives, while harmful activity that falls outside the rule produces no alert. Organizations already receive thousands of security alerts daily, so each unnecessary review competes with work on genuine threats. Flagged events that go uninvestigated can leave genuine threats undetected.
The Fraunhofer FKIE and RWTH Aachen risk-based alerting study explains why additional information matters. A crashing PDF reader, a new user account, and high outbound traffic may each mean little on their own. Their co-occurrence on the same system within one day warrants immediate review. Treating each event as an isolated binary trigger loses the relationship that makes the sequence worth investigating.
Analysts must then find the missing context themselves. Repeated triage of low-fidelity alerts crowds out threat hunting and compounds the pressure on teams with critical skills shortages. It also teaches analysts that an alert they have seen before usually comes from legitimate work. The analyst discounting the thousandth low-confidence bulk-copy alert may miss the copy that is not legitimate. Better tuning can reduce some noise, but it cannot supply information that the underlying rule never evaluates.
Four real cases where the rule-based gap became a breach
Former Intel employee Jinfeng Luo downloaded a large number of sensitive files just before termination. Intel’s DLP blocked one attempt, but he used a second device to complete the exfiltration. Intel sought significant damages after the data had left.
The Tesla case involved two former employees who leaked personal data of tens of thousands of employees to a German news outlet. Tesla’s official breach notification did not specify when the transfer occurred relative to their departure. The case concerns misuse by people with insider access, but that timing gap limits what can be concluded about departure-related monitoring. It does not establish that the transfer occurred during a notice period.
The GE engineer case involved substantial movement of sensitive information while the employee was negotiating departure and preparing to join a competitor. The engineer sent over 8,000 sensitive files to a personal email account, including design models, engineering drawings, and material data. The relevant context combined the transfer’s volume, the information’s value, and the employee’s departure.
In the multi-channel SaaS case, individually authorized activity across Slack, Salesforce, and Google Drive formed a pattern over four months. The signal existed in the combined activity.
How do modern insider threat platforms use behavioral context to catch threats that rules miss?
Behavioral context changes the unit of analysis from an isolated event to an action within a person’s working pattern. It evaluates the user, the data, the destination, the timing, and the surrounding activity together. Authorized access becomes the starting point for assessment.
Modern platforms build dynamic baselines for users and entities from telemetry across identity, endpoint, cloud, SaaS, and DLP systems. Those baselines represent normal activity against which new behavior can be scored. The distinction from a static threshold is specific. An event can deserve attention because it departs from the user’s history or role even when its volume remains ordinary.
A finance employee’s small downloads of engineering source code may not trigger a volume rule, but they can differ materially from the employee’s established work. The anomaly is the relationship between the identity and the content being accessed.
The same approach connects activity across channels and sessions. Slow movement through Slack, Salesforce, and Google Drive can contribute to a rising risk score even when every individual action is authorized. Lifecycle information gives more context when the way someone accesses data changes in the weeks around a resignation. A behavioral assessment can weight that period differently rather than judging the activity only against an unchanged event threshold.
Risk scoring brings suspicious signals together so an alert can surface when a composite score crosses a threshold, supported by the related activity that produced it. This makes the evidence for review more specific, while preserving the distinction between an anomaly and an established threat.
Why behavioral context still requires data understanding, not just behavior watching
A behavioral baseline establishes that activity has changed. Valuable intellectual property may carry no label because its sensitivity comes from its business meaning. Without content understanding, a system can score deviations involving quarterly projections and a source code repository without recognizing their different significance. Behavior supplies one dimension of risk.
A baseline can also miss an insider who moves valuable data at a rate that remains within their normal range. New employees, contractors, and embedded actors present the opposite problem because they have no established history from which to learn normal behavior. Historical comparison alone cannot resolve either case. The complete assessment must combine what the data means and whether its destination is appropriate with the person’s role, history, and surrounding activity. Adding behavioral analytics without that content context can still lead to both noise and missed threats.
How platforms that combine behavioral and content context change the analyst's job
Instead of reconstructing why a file movement matters, the analyst starts with the user’s activity, the relevant data, and the surrounding timeline. AI-assisted investigation can review events before they become alerts for people to check. This shifts the work from repeated triage to weighing the evidence and deciding whether it calls for escalation.
The Fraunhofer FKIE study found that risk-based alerting combining signals for the same entity achieved substantially higher alert prioritization performance than severity-level sorting alone. It also established a strong baseline for more complex LLM-based triage approaches. The distinction matters when evaluating AI-driven detection. The benefit comes from combining relevant evidence.
Candor combines understanding of the data with understanding of the person. It assesses what information means, where it is going, and whether that destination is appropriate given the content and the account, together with role, history, and surrounding behavior. Its multi-source behavioral profiles address the fragmented visibility that leaves authorized-channel abuse difficult to recognize. The platform assembles the investigation timeline before the event becomes a human alert, targeting mean-time-to-investigation.
For teams assessing implementation effort, Candor’s homepage FAQ states that most organizations are live within a single week depending on whether they select an on-premise or cloud deployment. Its stated function is limited to detecting suspicious data movement and assembling cases for review. That boundary matters when matching the platform to an operational need. Broader coverage is useful only if the resulting cases are manageable, explainable, and supported by an auditable evidence chain, especially when an alert names a person.
What a security team should actually evaluate when moving away from rule-only detection
Moving away from rule-only detection means deciding how the organization will handle insider risk as well as choosing a different product. The organization must first define who receives an alert and what authority that person has to act. An analyst needs a defined escalation path because informal disclosure and quiet closure both undermine the purpose of detection. An alert about a colleague affects the organization in ways that an ordinary host alert does not.
A migration, a busy quarter-end, or a period of unusual access can teach a model that exceptional activity is normal. Evaluation should therefore establish how the platform interprets its training period and handles users without sufficient history. Day-one risk from contractors, new employees, and embedded actors cannot depend entirely on a baseline that does not yet exist.
Content understanding deserves a separate test. The platform should distinguish activity involving valuable IP from routine bulk movement of low-sensitivity files rather than treating every deviation as equally important. Candor’s stated ability to identify suspicious data movement from day one without custom policies is relevant to that evaluation, but the governing criterion remains the same across options. The system must explain why the data, destination, and account make a particular movement worth reviewing.
Finally, detection must be explainable and auditable. A black-box score beside a person’s name is not an investigation, so the evidence chain must be visible enough to support responsible escalation. Detection rate alone cannot show whether the transition has worked. The practical measure is the average time it takes to begin an investigation. A platform that finds the right event but leaves analysts buried in triage still delays investigation.