 Insider Threat Detection
Ranking AI-Driven UBA Tools by the Behavioral Signals That Actually Surface Insider Threats
The best UBA tools fuse behavioral signals across time and systems to reveal intent, not noise.
Callum Ferreira·
 Insider Threat Detection
The 2025 Insider Threat Tool Landscape From a Security Engineer's Bench
Legacy tools miss the patterns that define real insider threats.
Renata Szymańska·
 Insider Threat Detection
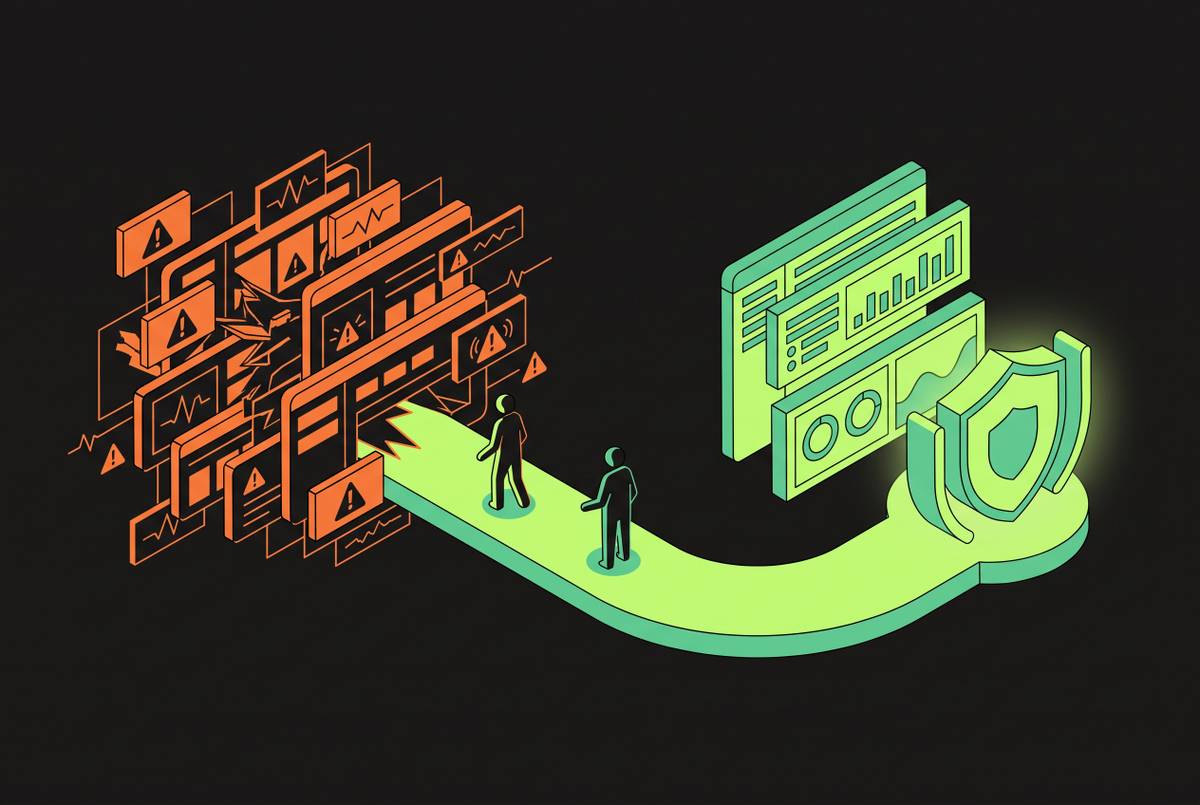
How Modern Insider Threat Platforms Are Redesigning the Alert From the Ground Up
Behavioral context and data meaning transform alerts from noise into investigation-ready cases.
Darius Okonkwo·
 Insider Threat Detection
The Security Team's Exit Ramp From a UEBA Deployment Drowning in False Positives
Statistical anomaly detection can't distinguish breaches from normal behavior changes.
Renata Szymańska·
 Insider Threat Detection
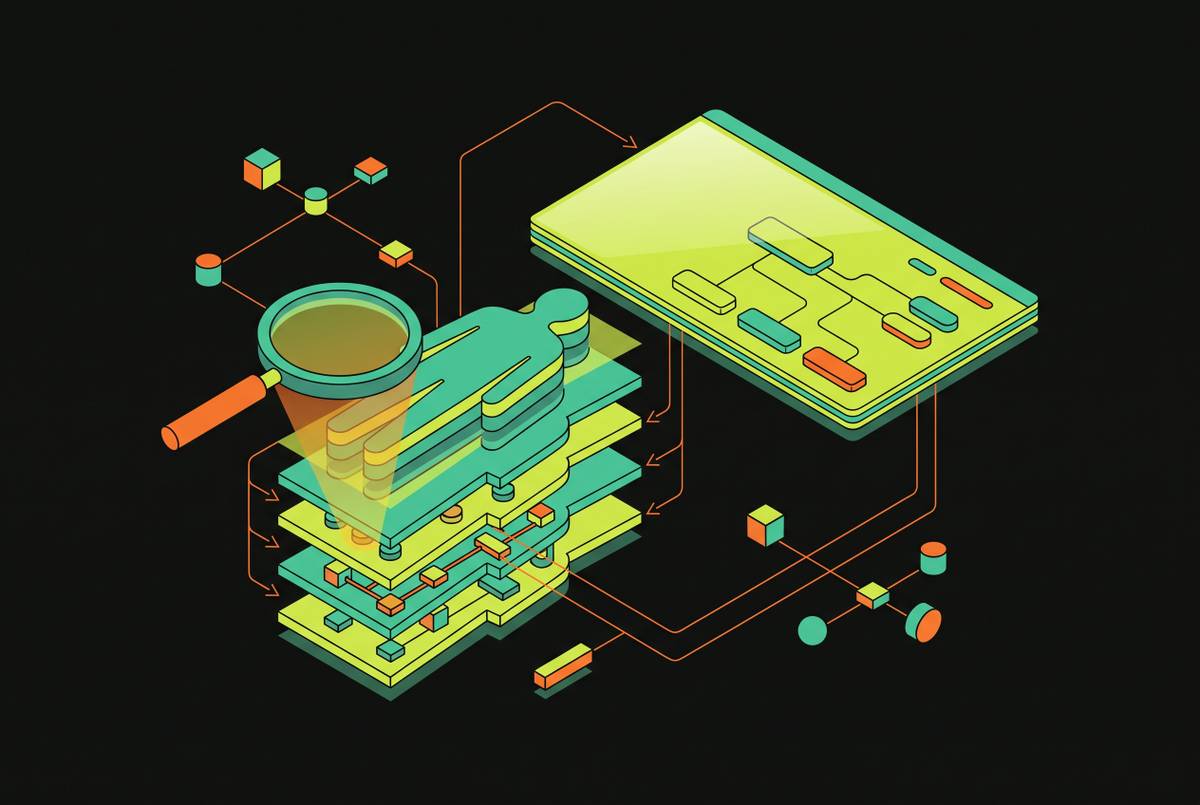
Scoring Insider Threat Platforms on Behavioral Context Depth, Not Dashboard Polish
Behavioral depth in threat detection matters far more than dashboard design.
Darius Okonkwo·
 Insider Threat Detection
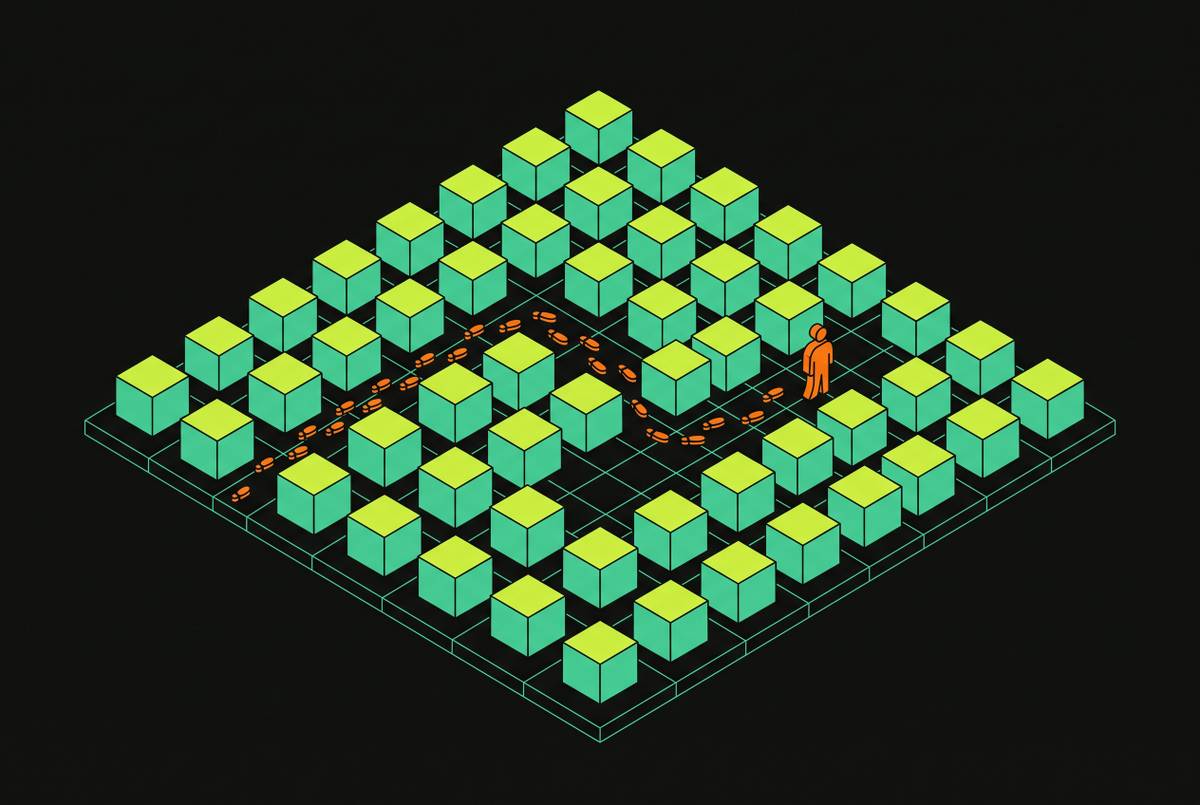
Why Static Rules Cannot Model the Behavioral Drift That Precedes Insider Incidents
Behavioral drift unfolds gradually across weeks—far slower than any single rule can detect.
Mei-Lin Tsao·
 Insider Threat Detection
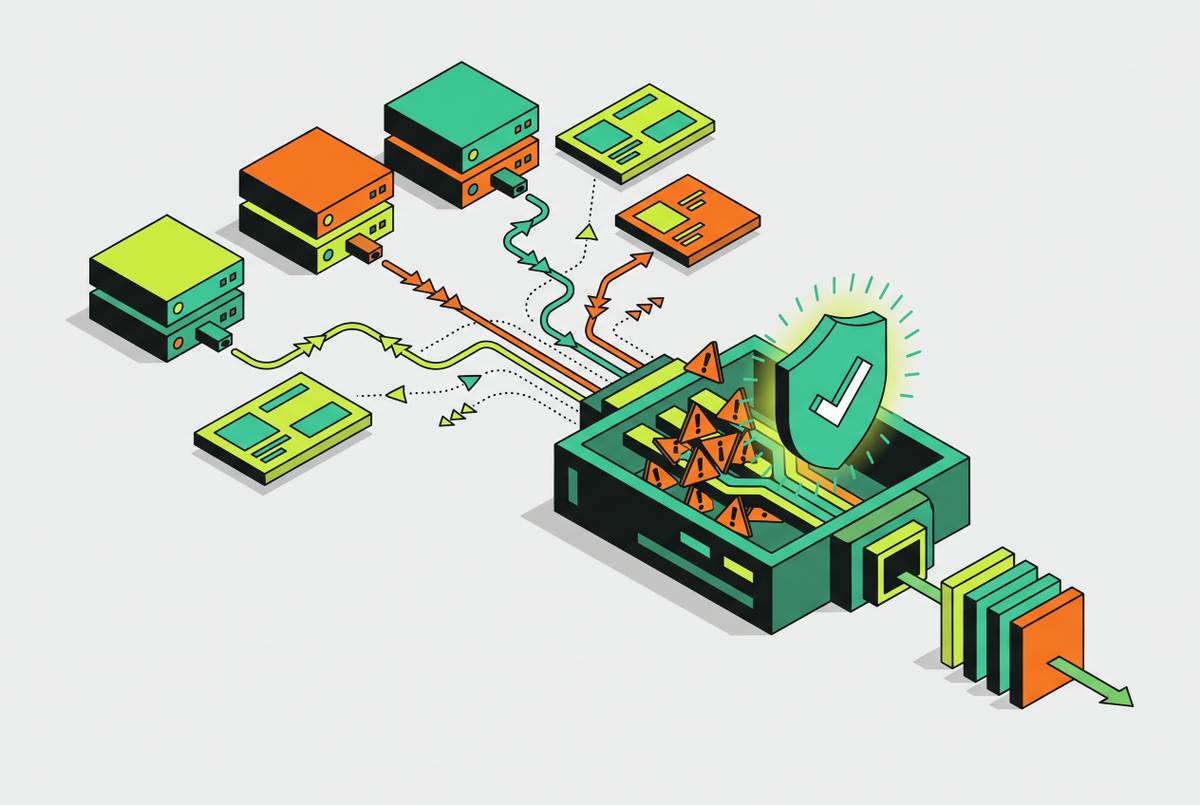
Why Cross-Source Behavioral Context Is the Real Fix for Insider Threat Alert Fatigue
Connecting identity, endpoint, and cloud signals reveals what single tools miss alone.
Darius Okonkwo·
 Insider Threat Detection
The Security Analyst's Checklist for Evaluating Modern Insider Threat Platforms Against Aging UEBA Deployments
Legacy UEBA misses modern insider threats moving through cloud and SaaS environments.
Mei-Lin Tsao·
 Insider Threat Detection
How Vendors Are Embedding AI Into Insider Threat Monitoring Without Multiplying False Positives
New AI tools evaluate user context and data meaning to slash insider threat false alarms.
Darius Okonkwo·
 Insider Threat Detection
How AI-Native Insider Threat Platforms Use Behavioral Analytics Instead of Static Alert Rules
Behavioral analytics catches threats by tracking patterns, not matching isolated events.
Callum Ferreira·
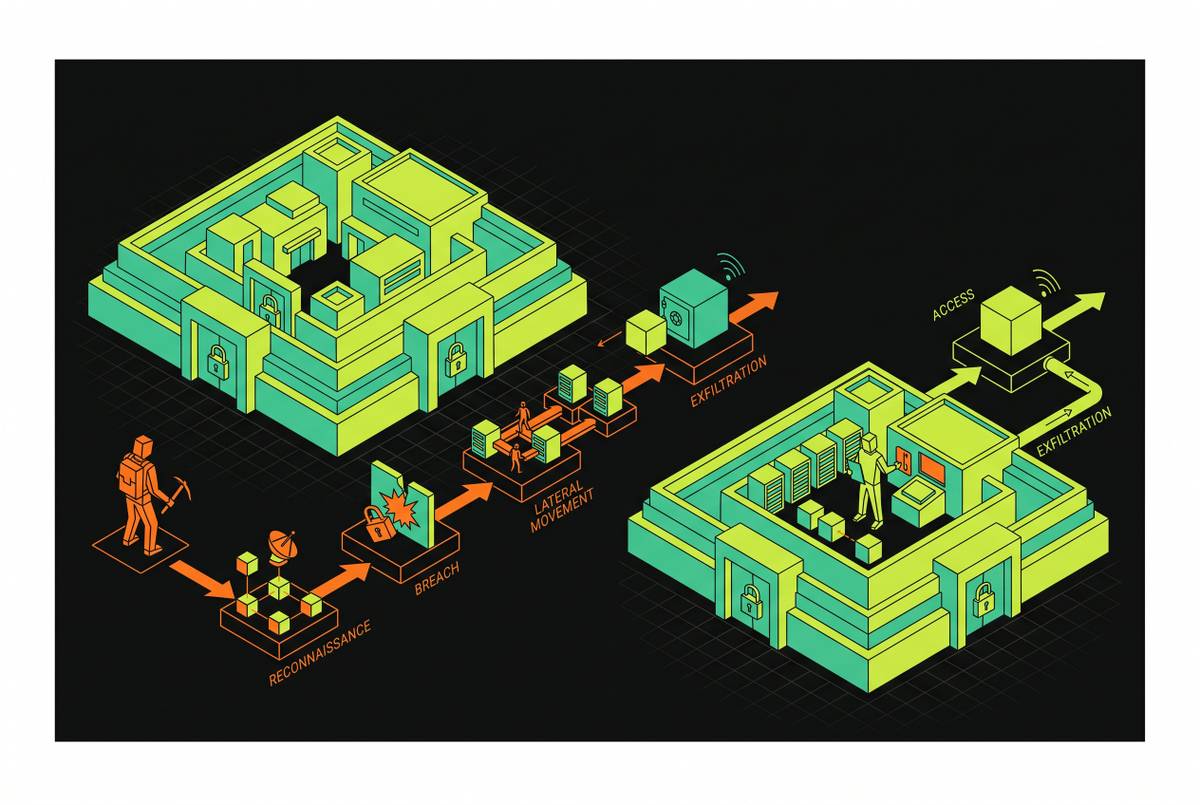 Insider Threat Detection
Insider Threat Kill Chain Compared to External Attack Kill Chains
Insiders bypass the kill chain because they start with access, not outside trying to get it.
Darius Okonkwo·
 Insider Threat Detection
Third-Party and Contractor Insider Risk in Enterprise Environments
Third-party contractors bypass the behavioral monitoring that catches employee insider threats.
Darius Okonkwo·
 Insider Threat Detection
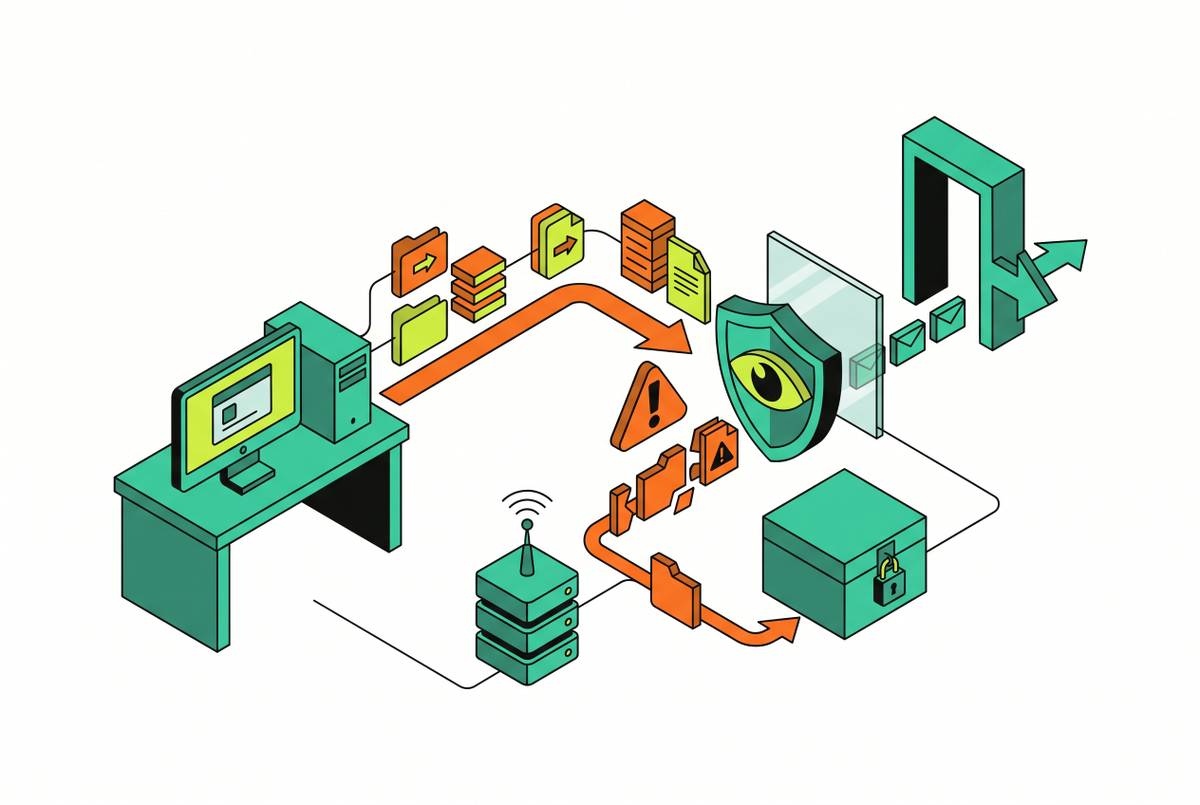
Detecting Data Exfiltration Before Employee Resignation
Employees steal data months before resigning, leaving a detectable behavioral arc.
Renata Szymańska·
 Insider Threat Detection
Insider Threat Indicators in Privileged User Accounts
Privileged accounts demand behavioral detection, not access rules, to catch insider abuse.
Mei-Lin Tsao·
 Insider Threat Detection
 in Remote and Hybrid Workforces
Old detection logic collapses when work leaves the office walls.
Renata Szymańska·
 Insider Threat Detection
Insider Threat Case Management Workflows for Security Teams
Implement structured case workflows to turn insider threat alerts into defensible investigations.
Mei-Lin Tsao·
 Insider Threat Detection
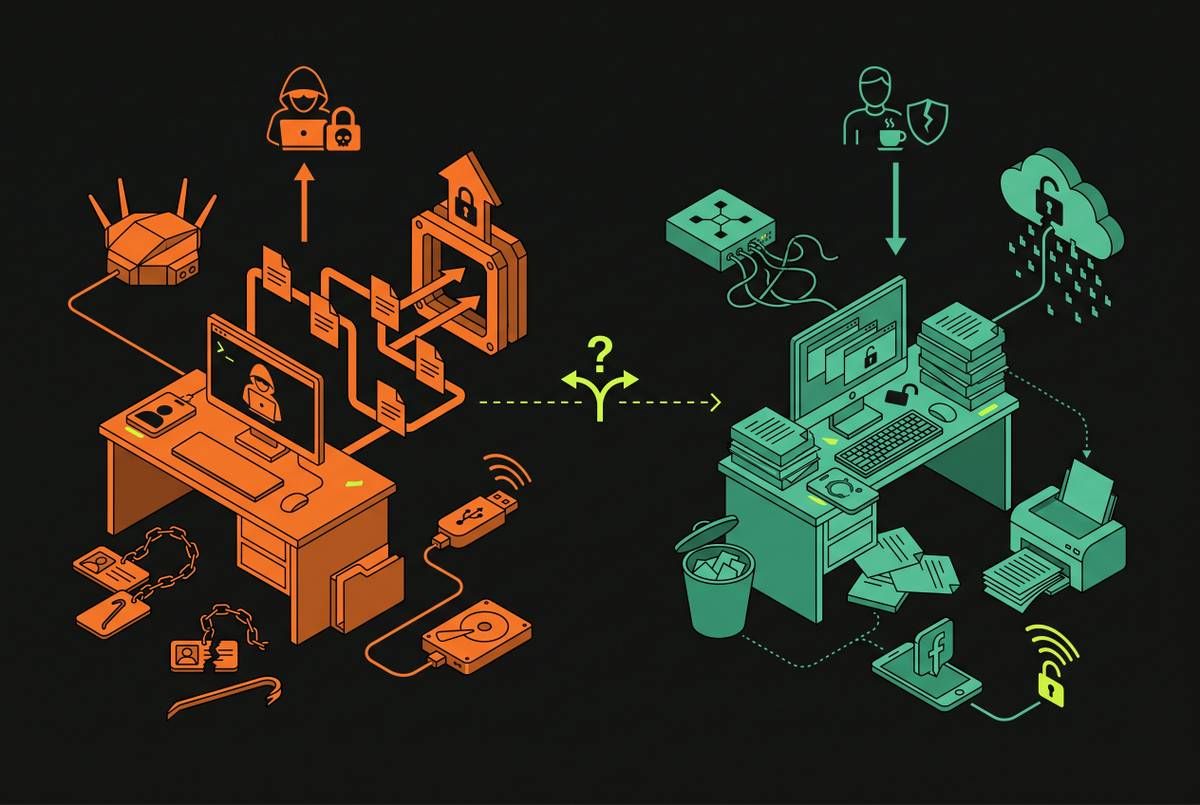
Behavioral Indicators of Malicious Insiders vs. Negligent Users
Context matters more than individual suspicious events when identifying insider threat types.
Darius Okonkwo·