Why Static Rules Cannot Model the Behavioral Drift That Precedes Insider Incidents
Behavioral drift unfolds gradually across weeks—far slower than any single rule can detect.
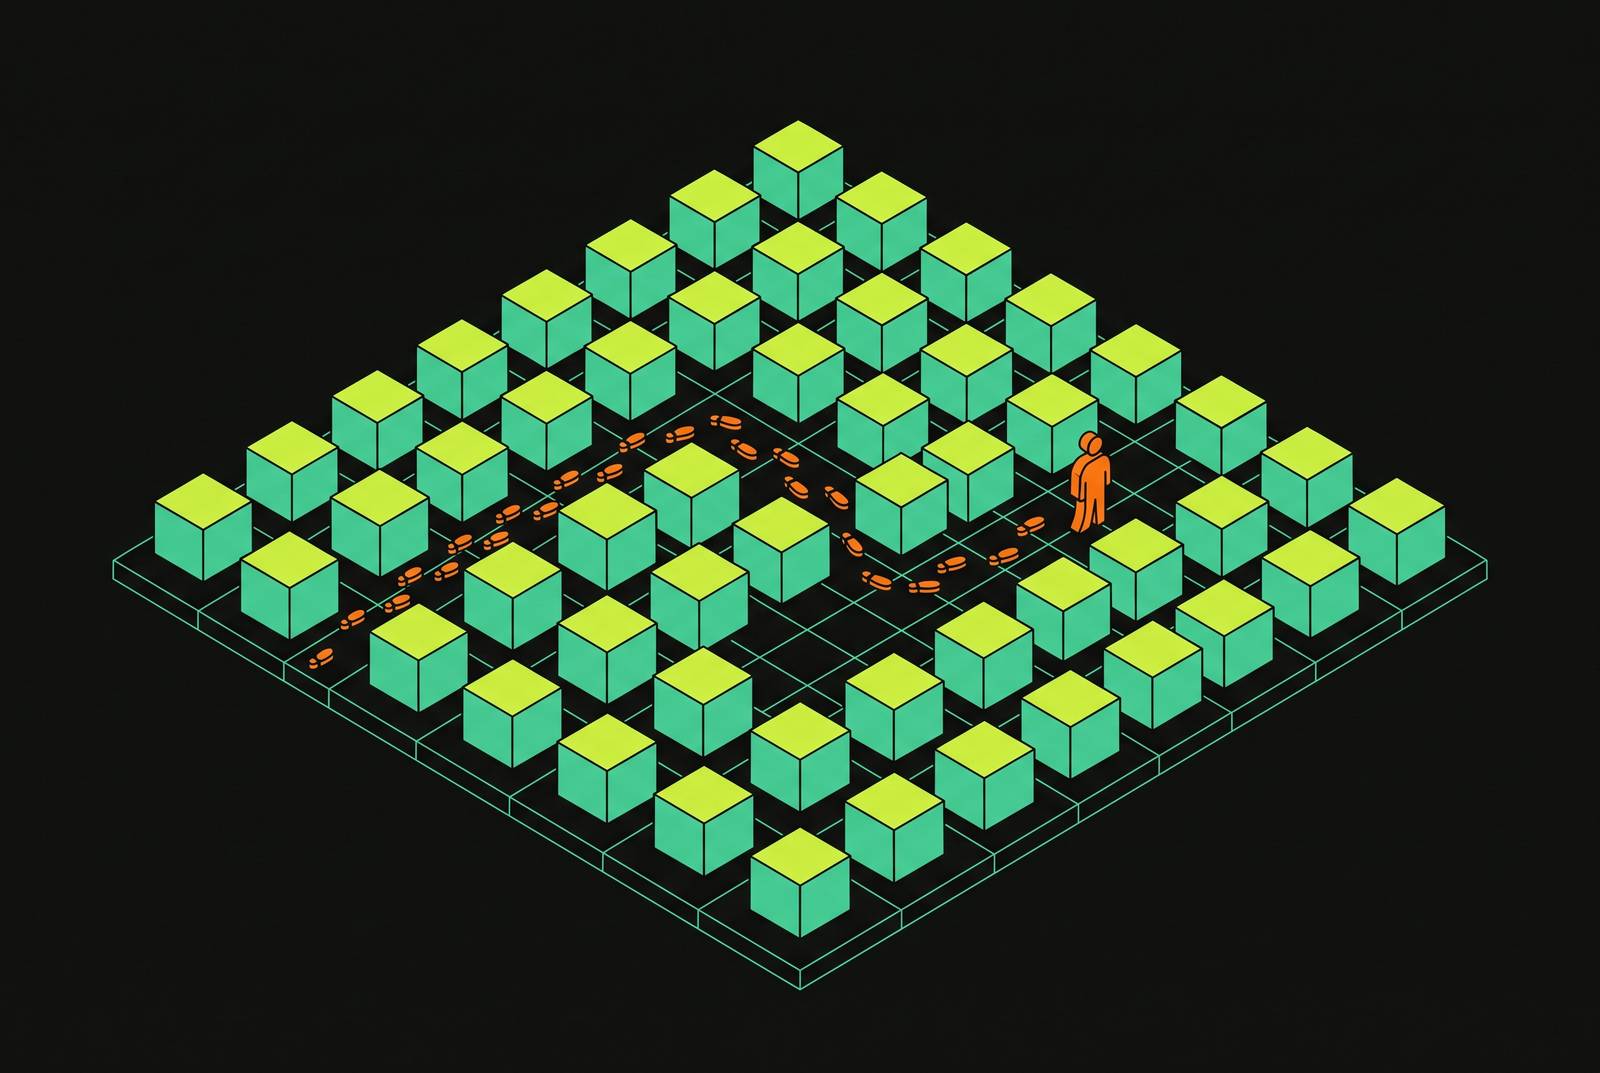
Static rule-based alerting can't catch insider threats, because the risk signal lives in behavioral drift, and there's no single event a rule can check that will show it. Insider incidents develop over days or weeks of gradual change across systems, and by the time a damaging act occurs, a long trail of individually authorized actions has already preceded it. The platforms that catch this pattern do so by modeling the timeline itself, not by checking discrete events against fixed thresholds.
Why insider incidents are preceded by drift, not detonation
An insider incident rarely begins at the moment it becomes visible. It begins earlier, in a slow change in behavior that unfolds across days or weeks before anyone moves a file that actually causes harm. The person behind that change is, in nearly every case, someone the organization has already trusted with access: an employee, a contractor, a business partner acting within the bounds of a legitimate account. That fact changes what the harmful signal actually is. The harmful signal is the pattern that surrounds the download or the login, not the act itself.
Behavioral data is noisy by nature. A file download at 11 p.m. means something different for a developer who regularly works late than it does for someone who has never logged in outside business hours. A single data point, read without its timeline, tells an analyst almost nothing. But put weeks of context around that same data point, and it can mean everything. That is what makes insider risk hard to catch: the signal is cross-system and cumulative, spread across login sessions, file access, process execution, and movement between cloud platforms, and no individual piece of it looks alarming on its own.
Think of a developer who pulls large volumes of source code outside normal hours, or an employee who, while planning to leave, starts moving customer lists to a personal device. Neither act, taken alone, triggers much concern. A developer downloads code. An employee accesses the customer list she's used for two years. The behavior only resolves into a threat signal when read across time, against what that person normally does, and against what changed around them. That's the structural question the rest of this piece works through: what kind of detection model can actually see a pattern like that, when every point along it looks legitimate?
What static rules are doing when they evaluate behavior
Rule-based systems compare an observed action against a predefined policy or a known bad pattern. Someone downloads a file larger than a set size, or copies data to an unapproved destination, and the rule checks that single event against a fixed threshold. The output is binary: the rule fires, or it doesn't.
This design isn't a mistake. Rule-based systems were built this way on purpose, because simplicity gives organizations something valuable: interpretability. A security team can read a rule, understand what it checks, explain to an auditor why it exists, and adjust it when a known policy changes. That transparency is why rule-based controls became the backbone of compliance-driven data loss prevention for two decades. They're auditable. They're predictable. They're easy to defend to a regulator who wants to know why a control exists.
The unit of analysis in this design is the event, not the person and not the timeline. A rule looks at what just happened and decides, with no memory of what came before it. Most current DLP approaches work this way: they enforce a static set of rules governing what a user can and cannot do with a given type of data, a model built for compliance enforcement rather than for judging risk based on behavior. Traditional DLP tools built on this foundation struggle to keep pace with hybrid cloud environments, and most of them run in silos, without real integration into SIEM, UEBA, or other automated threat platforms that might supply the missing context. None of this makes the rules badly engineered. It makes them suited to a narrower problem than the one insider threats actually present.
Why the architecture of static rules makes drift invisible
A static rule has no representation of time. It holds no trajectory, no memory of accumulation across systems, nothing but the state of one event at one moment. It's a structural limit built into what the architecture can compute, one that better thresholds could not close.
When an employee changes role, switches projects, or starts planning an exit, a rule written for today's definition of normal goes stale. Because these systems cannot adapt to new or evolving scenarios, their effectiveness decays as soon as the environment around them shifts. The deeper problem appears in sequences where each step, examined on its own, is fully authorized. A rule has nothing to fire against in that case, because nothing in the sequence violates policy until the pattern has already accumulated into something damaging.
A four-month case at the SaaS layer, documented in recent research, shows the mechanism directly. An insider exfiltrated customer lists, pricing details, and competitive intelligence by moving through Slack, Salesforce, and Google Drive, with employee personal data pulled separately through an HR system. Traditional DLP missed the entire sequence, because every individual action inside it appeared authorized at the time it happened. Concept drift lets behavior shift gradually enough to stay inside the noise band a rule is built to ignore, so a patient actor can sit inside that gap indefinitely. Even ensemble-based anomaly detection can inherit this weakness if it still relies on fixed thresholds and deterministic outputs, and that leaves little room for the ambiguous, partially-formed signals that insider activity actually produces.
What all of this comes down to is a gap in intent. Rule-based DLP can see that data moved. It cannot assess why, or whether the movement fits a person's role, their history, or the pattern building around them. An insider threat can stay completely visible in the logs and still go undetected, because visibility and understanding are not the same thing.
How drift-based incidents unfold: two documented patterns
Two patterns account for most drift-based insider incidents, and static rules miss both for the same underlying reason: each step inside them looks like ordinary, permitted behavior.
The first is pre-departure acceleration. In 2022, Qian Sang, a senior research scientist at Yahoo, downloaded hundreds of thousands of pages of confidential material related to Yahoo's AdLearn product, including source code, backend architecture, and proprietary algorithms. The download followed shortly after he received a competing job offer. The exfiltration itself was compressed into a short window, but it sat at the end of months of access that had been authorized the entire time.
The second is prolonged authorized access. In 2023, two former Tesla employees used internal IT system access to extract and transfer a large volume of confidential data, including the personal information of tens of thousands of current and former employees, to an external outlet. There was no single moment of escalation here. Privileged access was used over an extended period in a way that, examined action by action, matched normal behavior for people in those roles.
Both cases share the same structure. The risk was never located in one event. It was in the trajectory, the accumulation of access and movement across weeks or months that a system evaluating each event in isolation has no way to reconstruct.
The operational cost when rules miss drift: alert fatigue and delayed investigation
When static rules miss drift, the failure doesn't stay quiet. It produces noise, and that noise buries the real signal once it does cross a threshold. Unrefined thresholds, redundant rules, and legacy signatures that never got retired generate false positives at scale, and without constant tuning, detection quality degrades over time.
The population a security team actually has to watch makes this worse. Insider risk covers more than malicious employees. It includes negligent users, compromised accounts, contractors, and third parties, so the real set of events that matter is more varied than any fixed rule set can represent, and the false-positive surface widens accordingly. An analyst buried in false positives becomes less likely, not more, to chase the ambiguous, low-confidence signal that behavioral drift typically produces at the point it's still preventable. The detection failure and the triage failure feed each other.
Mean-time-to-investigation is where this cost becomes measurable. The longer the gap between an alert firing and an analyst actually looking at it, the further an exfiltration sequence can progress before anyone intervenes. Cutting that gap matters as much as improving raw detection accuracy, because a detection that arrives correctly but late still allows the damage it was meant to catch.
What a detection model must represent to catch drift
Catching drift means building a model that holds time, uncertainty, cross-system context, and identity together, none of which a static rule can represent at once.
Time has to become a first-class input. You need to build a behavioral baseline for each user and keep updating it, so you can see a trajectory toward risk even while every point along that trajectory still looks individually authorized. That means comparing behavior against a baseline that moves with the person, not a fixed profile set once and left alone.
Uncertainty has to be quantified and carried forward as part of the output. Hard clustering and deterministic rules force a crisp decision regardless of how much confidence the underlying data actually supports. A better approach estimates both a cluster assignment and the uncertainty behind that assignment, flagging ambiguous cases for a human to review while classifying high-confidence threats on its own. Research on real-time insider threat detection using behavioral analytics and deep evidential clustering reports 94.7% average detection accuracy with this dual approach, and it cuts false positives without a corresponding rise in false negatives.
Visibility has to span systems. Drift appears across email, cloud storage, SaaS applications, and endpoint activity together, so a model needs behavioral embeddings built across that whole stack, reading signals in combination. Detecting drift means treating the full timeline as the unit of analysis, reconstructing a pattern across multiple systems and weeks. Platforms like Candor build behavioral profiles across the enterprise stack instead of enforcing fixed thresholds on single actions, so they can surface that cross-system context before any individual action ever breaches a policy.
Identity and role belong in the decision too. The same data movement carries different risk depending on who's doing it, what their role actually authorizes, and what the rest of their activity looks like around it. Content, destination, identity, role, and surrounding behavior need to sit inside one decision, not five separate systems that never talk to each other.
None of this holds up operationally without explainability. A model that produces a risk score with no account of what drove it hands the investigation burden back to the analyst. The strongest objection to behavioral detection is a fair one: early UEBA deployments often generated excessive alerts from overly sensitive anomaly scoring, recreating the same fatigue problem rules were supposed to solve. Uncertainty-aware scoring paired with investigation the system completes on its own, before anything reaches a human queue, closes that gap.
How platforms that model behavioral drift differ in practice
Platforms built to catch behavioral drift differ from rule-based tools in more than their underlying algorithm. They differ in what gets handed to an analyst, and in how much of the investigation work is already finished by the time it arrives.
Candor is an AI-powered data loss prevention and insider risk platform built to understand both the data in motion and the person moving it: what the information actually means, where it's headed, who's interacting with it, and the pattern of activity surrounding that person across their timeline. It pairs modern DLP controls, including protection against shadow AI use and sensitive data leaks, with behavioral detection and investigation that spans enterprise systems, so it doesn't just watch one platform at a time. The platform surfaces suspicious data movement from day one, even without custom policies configured, by reading what's moving, where it's going, and the behavior around it rather than matching activity against a fixed rule set. Instead of handing an analyst a flood of alerts, it surfaces the movement that actually matters with the investigation largely assembled already, which cuts mean-time-to-investigation by finishing much of the work before a human ever opens the case. Teams that need tighter control can add policies in plain English, without a months-long deployment cycle or a dedicated team of rule authors, and the platform is built to go live in about a week rather than months, on-premise or in the cloud. Because detection decisions come with the contributing behavioral factors attached rather than a bare score, the output stays auditable instead of becoming another black box analysts have to take on faith. Coverage extends across the full population that insider risk actually involves: malicious employees, negligent users, compromised accounts, contractors, third parties, and AI agents, not just the narrower slice of events a fixed rule set could ever trigger on.
Vectra AI addresses cross-system visibility with a focus on identity-based risk signals, and you can use it for detection across hybrid environments where identity and infrastructure span multiple platforms at once.
Fidelis Security takes a different technical route. Fidelis Network uses Deep Session Inspection to reassemble entire communication sessions in real time, and this captures context across ports and protocols that fragmented packet-level inspection typically misses. The platform integrates UEBA with continuous behavioral monitoring to catch slow, multi-stage insider activity, and it adds deception technology to cut down on false positives.
What separates these platforms from rule-based tools is whether the platform resolves ambiguity, assembles cross-system context, and completes investigation work before an alert ever lands on an analyst's desk.
What security teams should change about evaluating detection coverage
When you judge an insider threat program, the right question is the shortest behavioral trajectory toward a damaging act that the tool can reconstruct across systems, from the first small deviation to the point where it would have become unrecoverable. A program that can only answer that question in hindsight, after the damage is already done, has the same structural blind spot static rules have always had.
Sources
- Real-Time Detection of Insider Threats Using Behavioral ...
- Real-Time Detection of Insider Threats Using Behavioral Analytics and Deep Evidential Clustering
- Mitigating Insider Threats and Data Breaches: Enhancing Data Loss Prevention Systems with Behavioral Analytics And NLP
- Can Risk-Based Alerting Mitigate Cybersecurity Alert Fatigue?
- AI-Driven Security Alert Screening and Alert Fatigue Mitigation in Security Operations Centers: A Survey